Engineering consultancy · Hanoi, Vietnam
Cloud. DevSecOps. Data & AI. Built as code, run by your team.
We set up governed landing zones, delivery pipelines with security gates, and data and AI platforms, as code in your repositories for your engineers to run and change.
Multi-Cloud Consulting
Policy, network, identity and cost decided once, then inherited by every workload.
- AWS
- Microsoft Azure
- Google Cloud
- On-premises & hybrid
DevSecOps
Scans and quality checks run as gates, and each failure goes to its owner.
- Cloud-native DevOps
- CI/CD pipelines
- Infrastructure automation
- Security integration
Data & AI
Governed data platforms, tested pipelines and AI measured before each release.
- Data platforms
- Data engineering
- Analytics
- AI solutions
What the published work shows
What the published work shows
Where programmes stall
The foundation sets the cost of everything built on it
Each of these starts as a reasonable local decision in an estate that grew one project at a time. None of them is fixed by adding a tool.
01
Every workload builds its own foundation
Each project settles its own networking, identity, policy and tagging. Address spaces overlap, firewall rules drift, and proving which subscriptions enforce a control takes an investigation.
02
Controls added after the design
Security controls arrive once the architecture is fixed. What should have been a design decision becomes a migration, and every exception is argued case by case.
03
Scans that report but never block
Scanning after the build produces a report, not a gate. Findings land at release, when they cost most to fix and are easiest to waive, and no one team owns them.
What we do
Three practices, each handed over as code
We keep to three practices. In each, the work ends as code, pipelines and runbooks in your repositories, for your team to run.
Multi-Cloud Consulting
What we do
Cloud foundations on AWS, Azure, Google Cloud or a hybrid estate: one governance model for hierarchy, policy, network, identity and cost, defined in Terraform your platform team owns.
Technology
- Azure
- Google Cloud
- Terraform
- Azure DevOps
Business value
Governance, network and cost decided once in code, then inherited by every workload on every platform.
DevSecOps
What we do
Delivery pipelines with SCA, SAST, image scanning and quality checks running as gates, Terraform for the infrastructure, and one image promoted from SIT to UAT to PROD.
Technology
- Google Cloud
- Kubernetes
- Terraform
- GitLab
Business value
Security and quality findings block the merge that caused them, and each one reaches the team that owns it.
Data & AI
What we do
Data platforms, pipelines as code, a semantic layer with agreed metrics, and AI applications with evaluation that gates each release, all under governance your team runs.
Business value
One agreed definition of each metric and governed access, so analytics and AI answers can be checked.
Why NinetyX
What you can hold us to
Independent of any one cloud
We start from your estate and your constraints, not a vendor's roadmap. The same governance model of hierarchy, policy, network and identity applies on Azure, Google Cloud, AWS or a hybrid estate.
Architecture before build
Work runs in order: strategy, architecture, implementation, then optimisation. Ownership, network and controls are settled and signed off before code is written, so the build inherits those decisions.
Security designed in
Controls are designed while the architecture is still open, and scans run inside the pipeline as gates. A failed check stops promotion and goes to whoever owns it: development, QA or security.
Judged by what you keep
We start from the decision your organisation needs to make. The measure is what stays when we leave: code in your repositories, runbooks, decision records and your own engineers able to run it.
Data and AI you can check
Data and AI work follows the same discipline. Zones are governed, transformations are tested and traced, metrics are defined once, and AI is measured against your questions before release.
Technology we work in
Technology we work in
Groups show which practice uses each technology. Status shows production history: ‘Run in production’ marks tools taken to production in our published work, and ‘Offered, not in published work’ marks tools we offer beyond it.
Cloud & Platform
Run in production
- Azure
- Google Cloud
- Terraform
- Azure DevOps
Offered, not in published work
- AWS
DevSecOps
Run in production
- Google Cloud
- Kubernetes
- Terraform
- GitLab
How we work
Four steps, each ending in something you review
01
Assess and scope
We review your current estate, delivery process and constraints with your engineers, then agree the scope, the owners and the decisions that have to come first.
02
Design and sign-off
We write down the architecture, the controls and who owns each part. Your team reviews and signs it off before any infrastructure or pipeline code is written.
03
Build in your repositories
We build as code in your repositories and through your change process, so your engineers review each increment as it lands rather than at the end.
04
Hand over and tune
We hand over runbooks and decision records and work alongside your engineers until they run it themselves. Then we tune cost, performance and controls with you.
Published work
Platforms that auditors and engineers can both follow
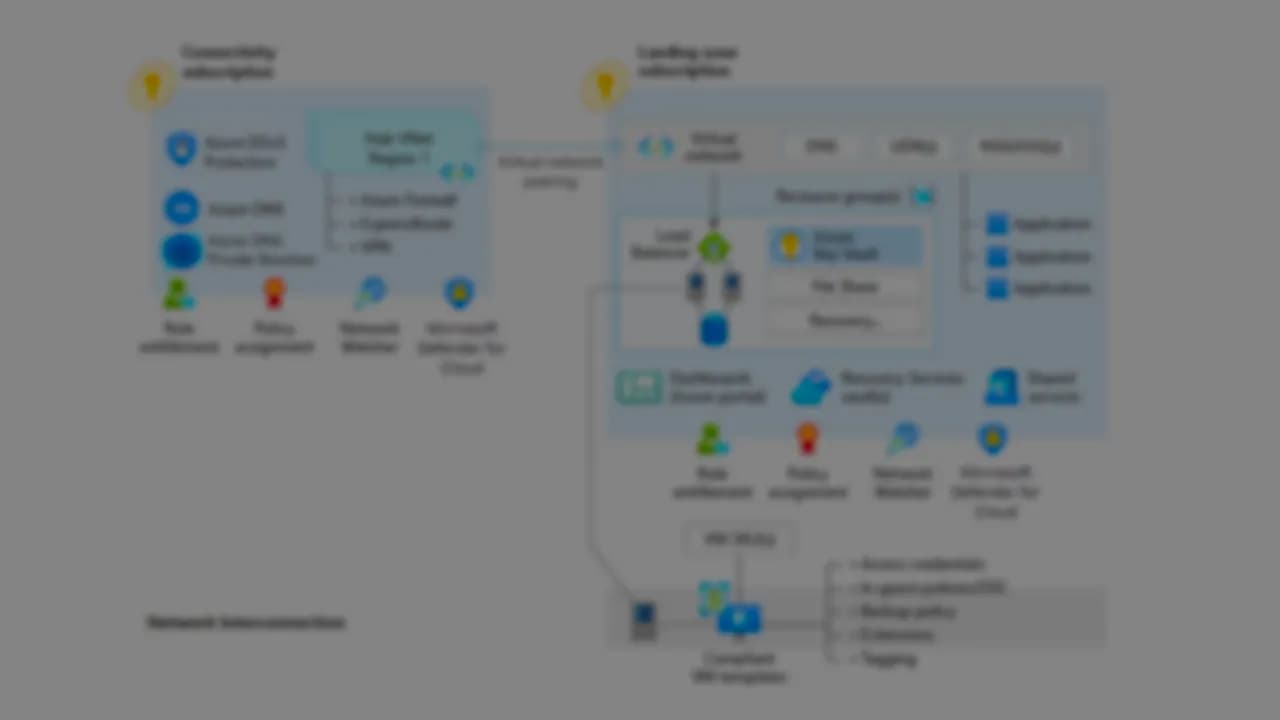
A governed Azure foundation a bank could build on
We designed and built an Azure landing zone for a bank: governance, hub-and-spoke networking, security policy and Terraform-delivered infrastructure.
We delivered a scalable, secure and efficient Azure landing zone that accelerated the bank's cloud adoption. Application teams deploy into subscriptions that already carry networking, policy, monitoring and backup, which…
- Azure
- Terraform
- Azure DevOps
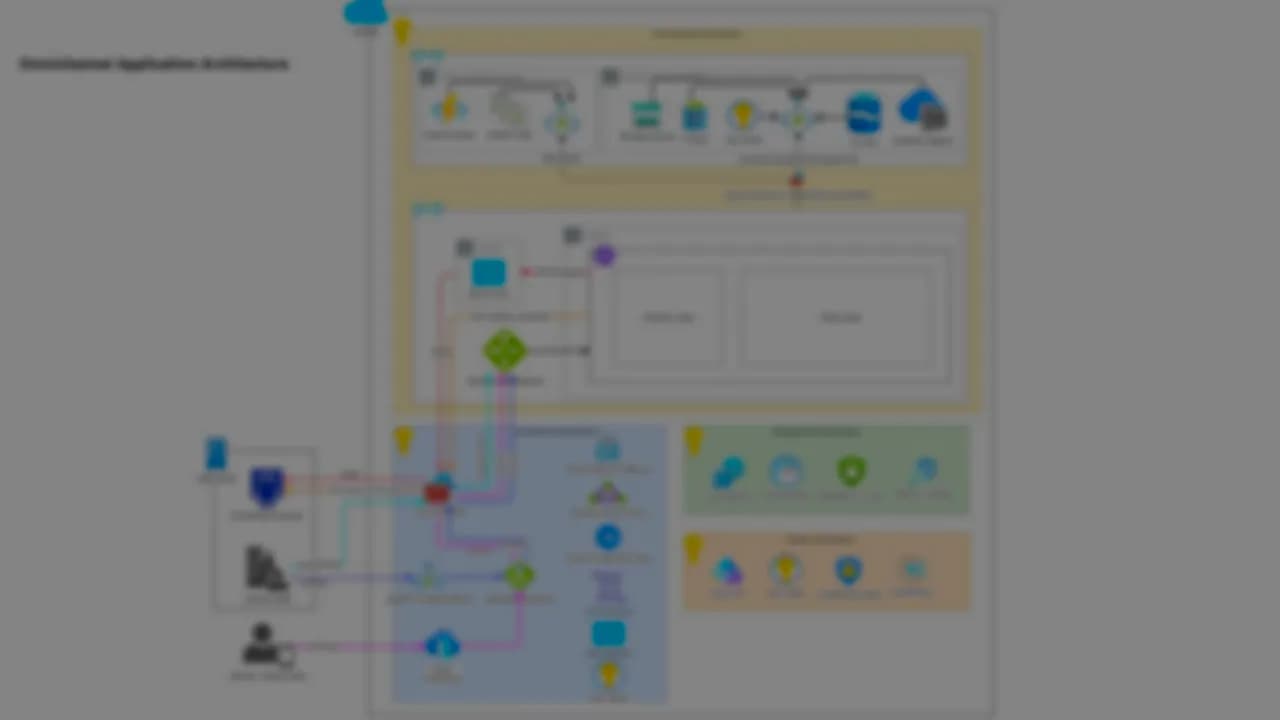
Omnichannel banking on Microsoft Azure, private by default
An omnichannel banking platform on Azure: one controlled edge for every channel, workloads on AKS, and data services reached only through private endpoints.
We delivered a scalable, secure and efficient application architecture on Microsoft Azure. Every channel enters through one controlled edge and every data service is reachable only through a private endpoint,…
- Azure
- AKS
- Front Door
- Keycloak
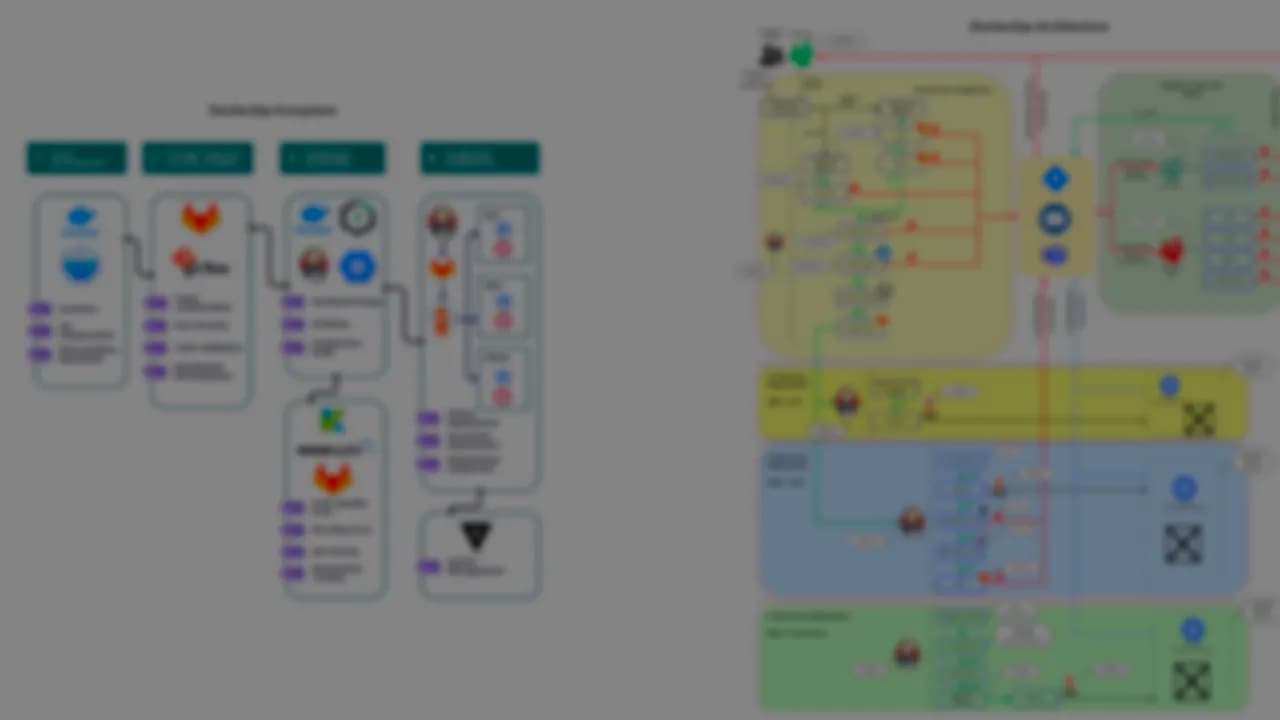
Security gates inside every pipeline, not after them
A DevSecOps delivery platform with GitLab, Jenkins and Argo CD on GKE, where every quality and security check is a pipeline gate owned by a named team.
The platform is designed to let teams release more often without letting security and quality review fall behind. Because checks run inside the pipeline and every failure reaches its owner…
- Jenkins
- Argo CD
- GKE
- GitLab
Blog
What we are working through
Laying out a Microsoft Fabric lakehouse for analytics
Fabric puts the lake, the warehouse and Power BI on one storage layer. That only simplifies things if medallion layers, workspace ownership and Direct Lake models are settled before the first load.
· 3 min read
Migrate the operating model, not just the workloads
Cloud programmes rarely stall on technology. They stall when workloads move but tickets, change windows and environment requests stay the same. Sequence by capability and run the landing zone as a product.
· 2 min read
Governed data comes before useful AI
AI work stalls in the data layer far more often than in the model. A catalogue, access granted at the source and lineage you can query are the groundwork most plans leave out.
· 2 min read
Start from the platform you have today
Tell us what you run, what is holding back the next release or workload, and who owns it. An engineer replies with questions and a proposed first step.