Published work
Cloud and DevSecOps work, with the constraints left in
Each write-up covers the starting point, the governance and audit context, the architecture as delivered and the stack. Client names are withheld under non-disclosure agreements; the technical detail is not.
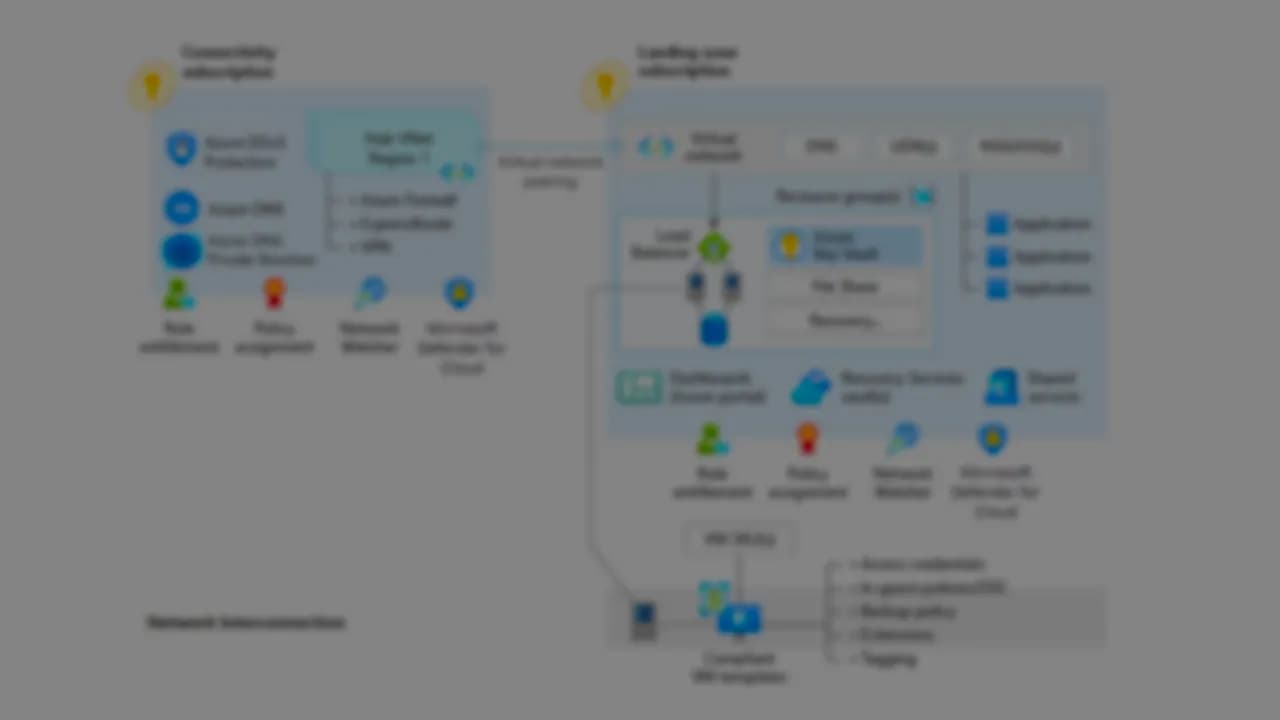
A governed Azure foundation a bank could build on
We designed and built an Azure landing zone for a bank: governance, hub-and-spoke networking, security policy and Terraform-delivered infrastructure.
We delivered a scalable, secure and efficient Azure landing zone that accelerated the bank's cloud adoption. Application teams deploy into subscriptions that already carry networking, policy, monitoring and backup, which…
- Azure
- Terraform
- Azure DevOps
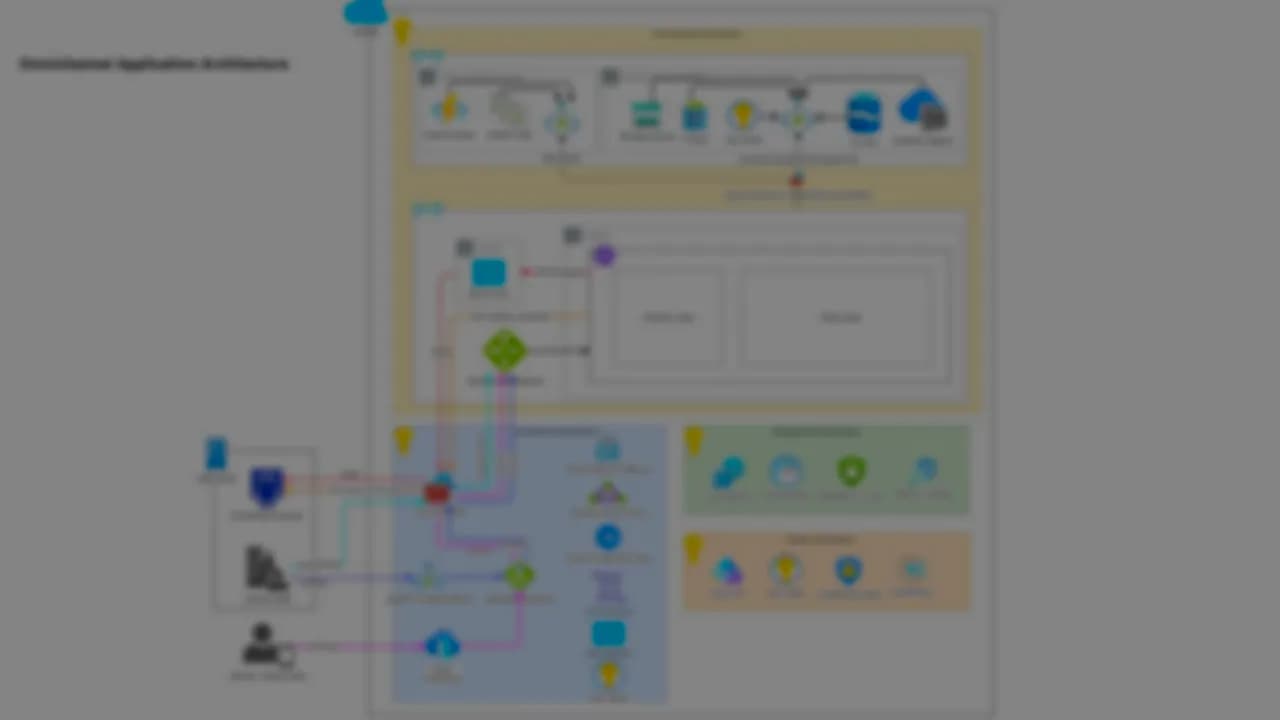
Omnichannel banking on Microsoft Azure, private by default
An omnichannel banking platform on Azure: one controlled edge for every channel, workloads on AKS, and data services reached only through private endpoints.
We delivered a scalable, secure and efficient application architecture on Microsoft Azure. Every channel enters through one controlled edge and every data service is reachable only through a private endpoint,…
- Azure
- AKS
- Front Door
- Keycloak
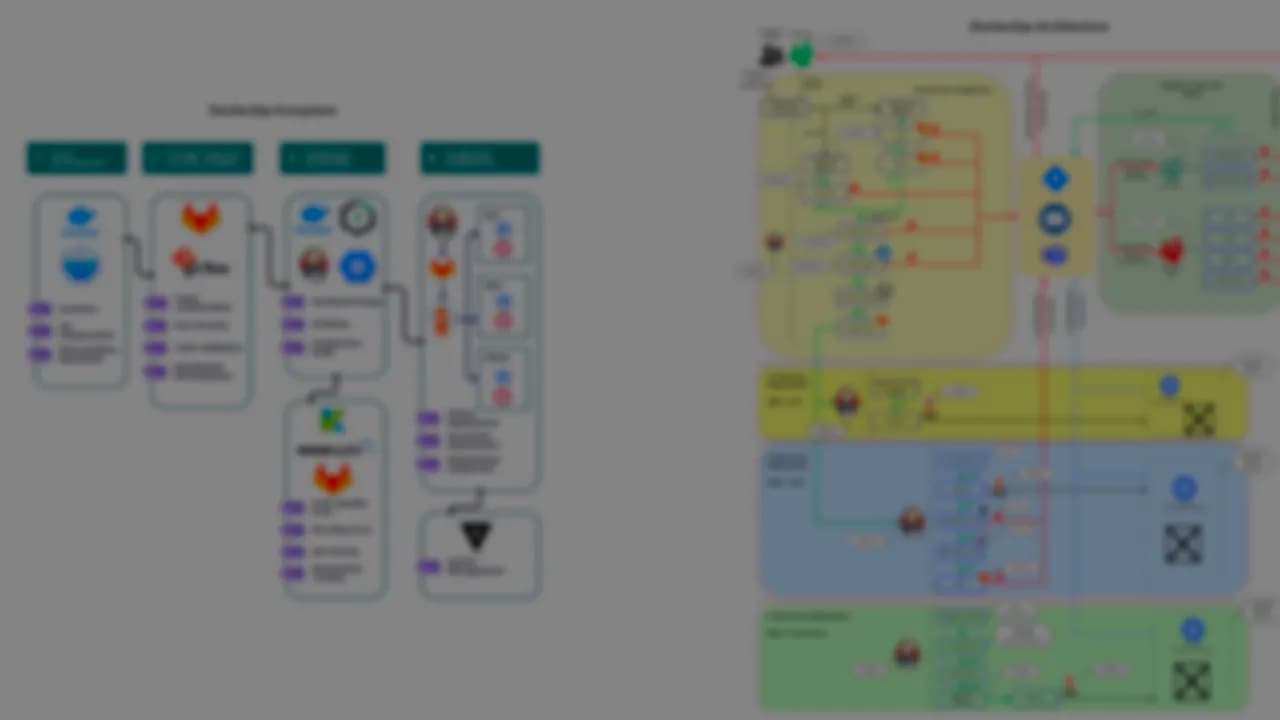
Security gates inside every pipeline, not after them
A DevSecOps delivery platform with GitLab, Jenkins and Argo CD on GKE, where every quality and security check is a pipeline gate owned by a named team.
The platform is designed to let teams release more often without letting security and quality review fall behind. Because checks run inside the pipeline and every failure reaches its owner…
- Jenkins
- Argo CD
- GKE
- GitLab
Start from the platform you have today
Tell us what you run, what is holding back the next release or workload, and who owns it. An engineer replies with questions and a proposed first step.